Skip to content
@khaleddevsecFull-Stack • Security • Engineering
Md Khaledul IslamCybersecurity & Software

I ENGINEER SOFTWARE
WITH SECURITY
BUILT IN.

I build web applications and security automation tools. My work combines full-stack development, application security testing, and custom tooling using technologies such as Go and Python.

Based in Bangladesh Focus Web + Security Approach Practical & secure Status Available for selected projects
Md Khaledul Islam (@khaleddevsec) — Cybersecurity Engineer & Full-Stack Developer
OPSEC // READY
01 / Selected work

See what I build.

Selected applications and security tools — deployed, tested, and verifiable.
01

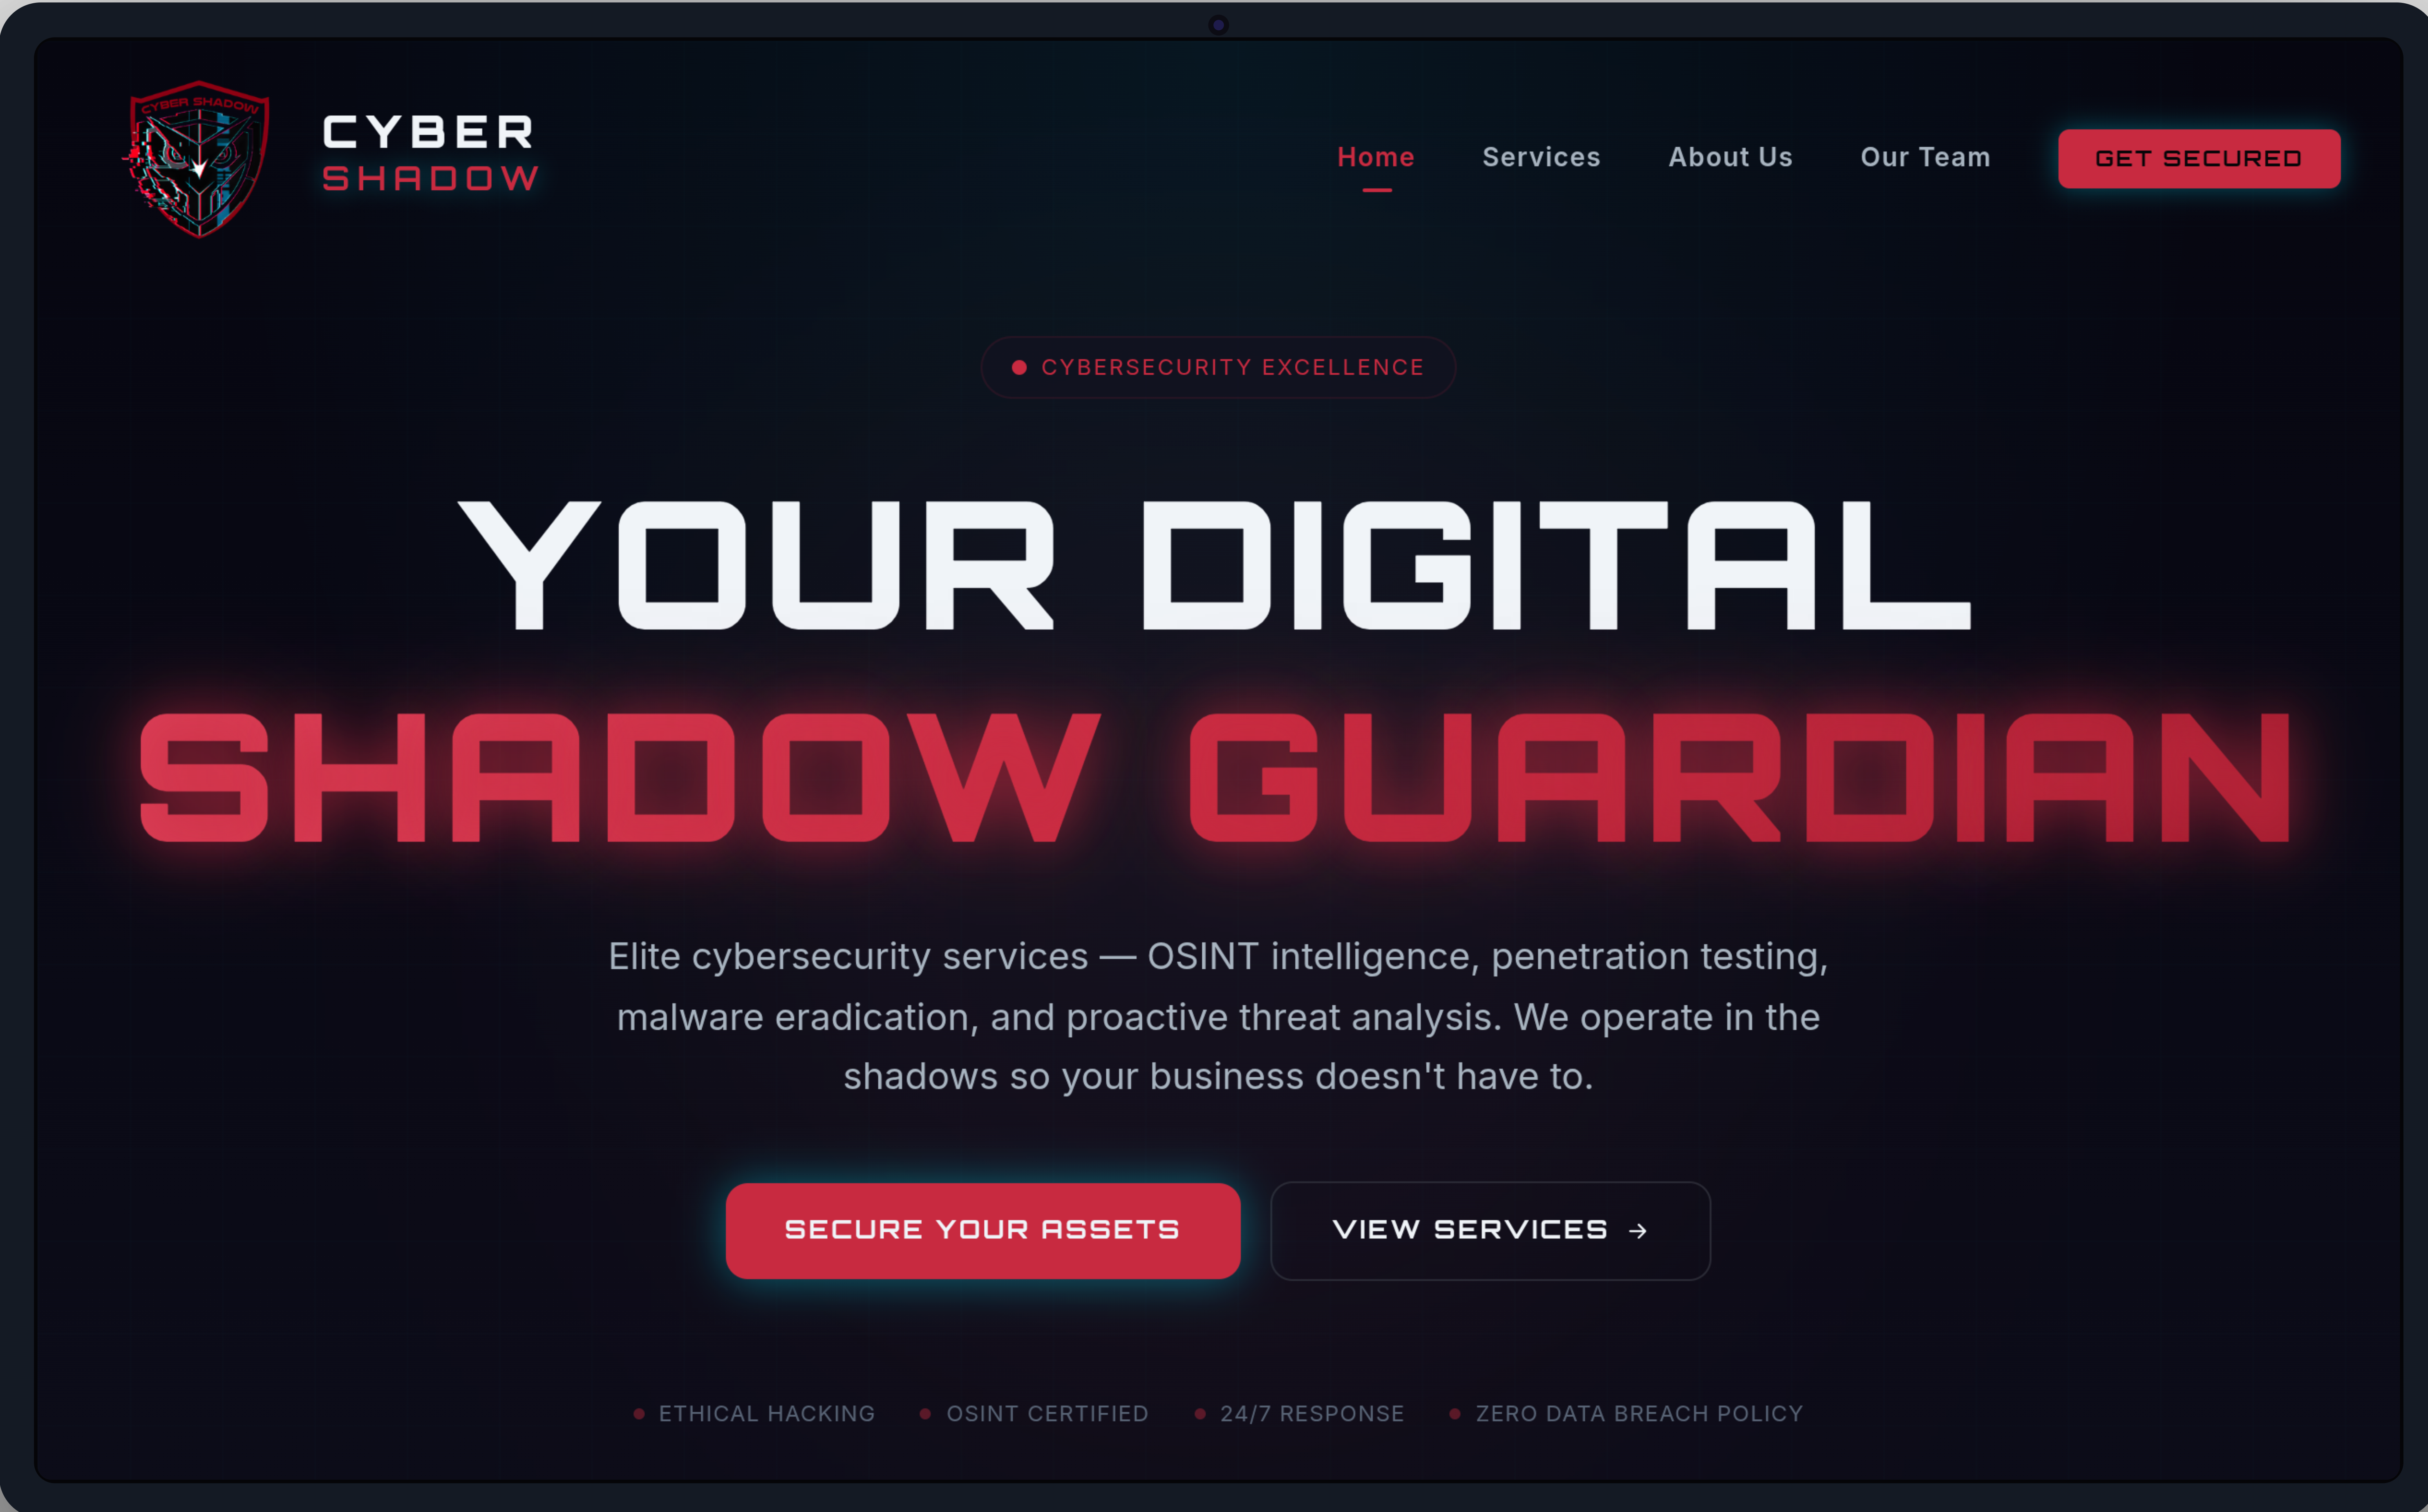
CYBER SHADOW

Web platform developed for Cyber Shadow to present the organization's cybersecurity services, assessment inquiry workflows, and technical resources.
VIEW SITE ↗
NEXT.JSTYPESCRIPTSECURITY PLATFORMCLIENT WORKFLOWS
https://cybershadow.info
VIEW SITE ↗
Cyber Shadow security platform interface preview
02

RECONPIPELINE

Go-based command-line tool for Linux that automates subdomain discovery, HTTP probing, crawling, and endpoint categorization into a repeatable reconnaissance workflow.

VIEW REPO ↗
GOLANGLINUXCLI TOOLINGOSINT & RECON
github.com/khaleddevsec/Reconpipeline
VIEW CODE ↗
Reconnaissance Pipeline
ACTIVE RUN
$ reconpipeline target.example.com
→ loading discovery engines: subfinder, assetfinder
→ passive enumeration ......... 142 subdomains
→ httpx active probing .......... 98 live hosts
→ katana deep endpoint crawl .... 1,840 URLs
→ merge, deduplicate & filter ... done
→ categorize endpoints .......... done

[+] Pipeline completed successfully
results output → /results/target.example.com/
DISCOVERYActive & Passive
PROBINGHTTP / HTTPS
CRAWLINGDeep & Archive
OUTPUTStructured
03

DORKX

Open-source Go CLI tool for automated search-engine dorking, parsing query operators and extracting clean, deduplicated target URLs for reconnaissance.

VIEW REPO ↗
GOLANGOSINT & DORKINGCLI TOOLINGAUTOMATION
github.com/khaleddevsec/DorkX
VIEW CODE ↗
DorkX OSINT Terminal
ACTIVE RUN
$ dorkx -q "site:target.com filetype:env" -o results.txt
→ querying search engine index endpoints
→ parsing query operators and patterns ... valid
→ collecting target URL candidates ...... 86 found
→ normalizing and filtering unique URLs .. 54 targets

[+] DorkX completed: unique target URLs written to results.txt
status → verified | format → plain text / json
PARSEROperators
INDEXINGSearch Endpoints
FILTERDeduplicated
OUTPUTCLI & File
04

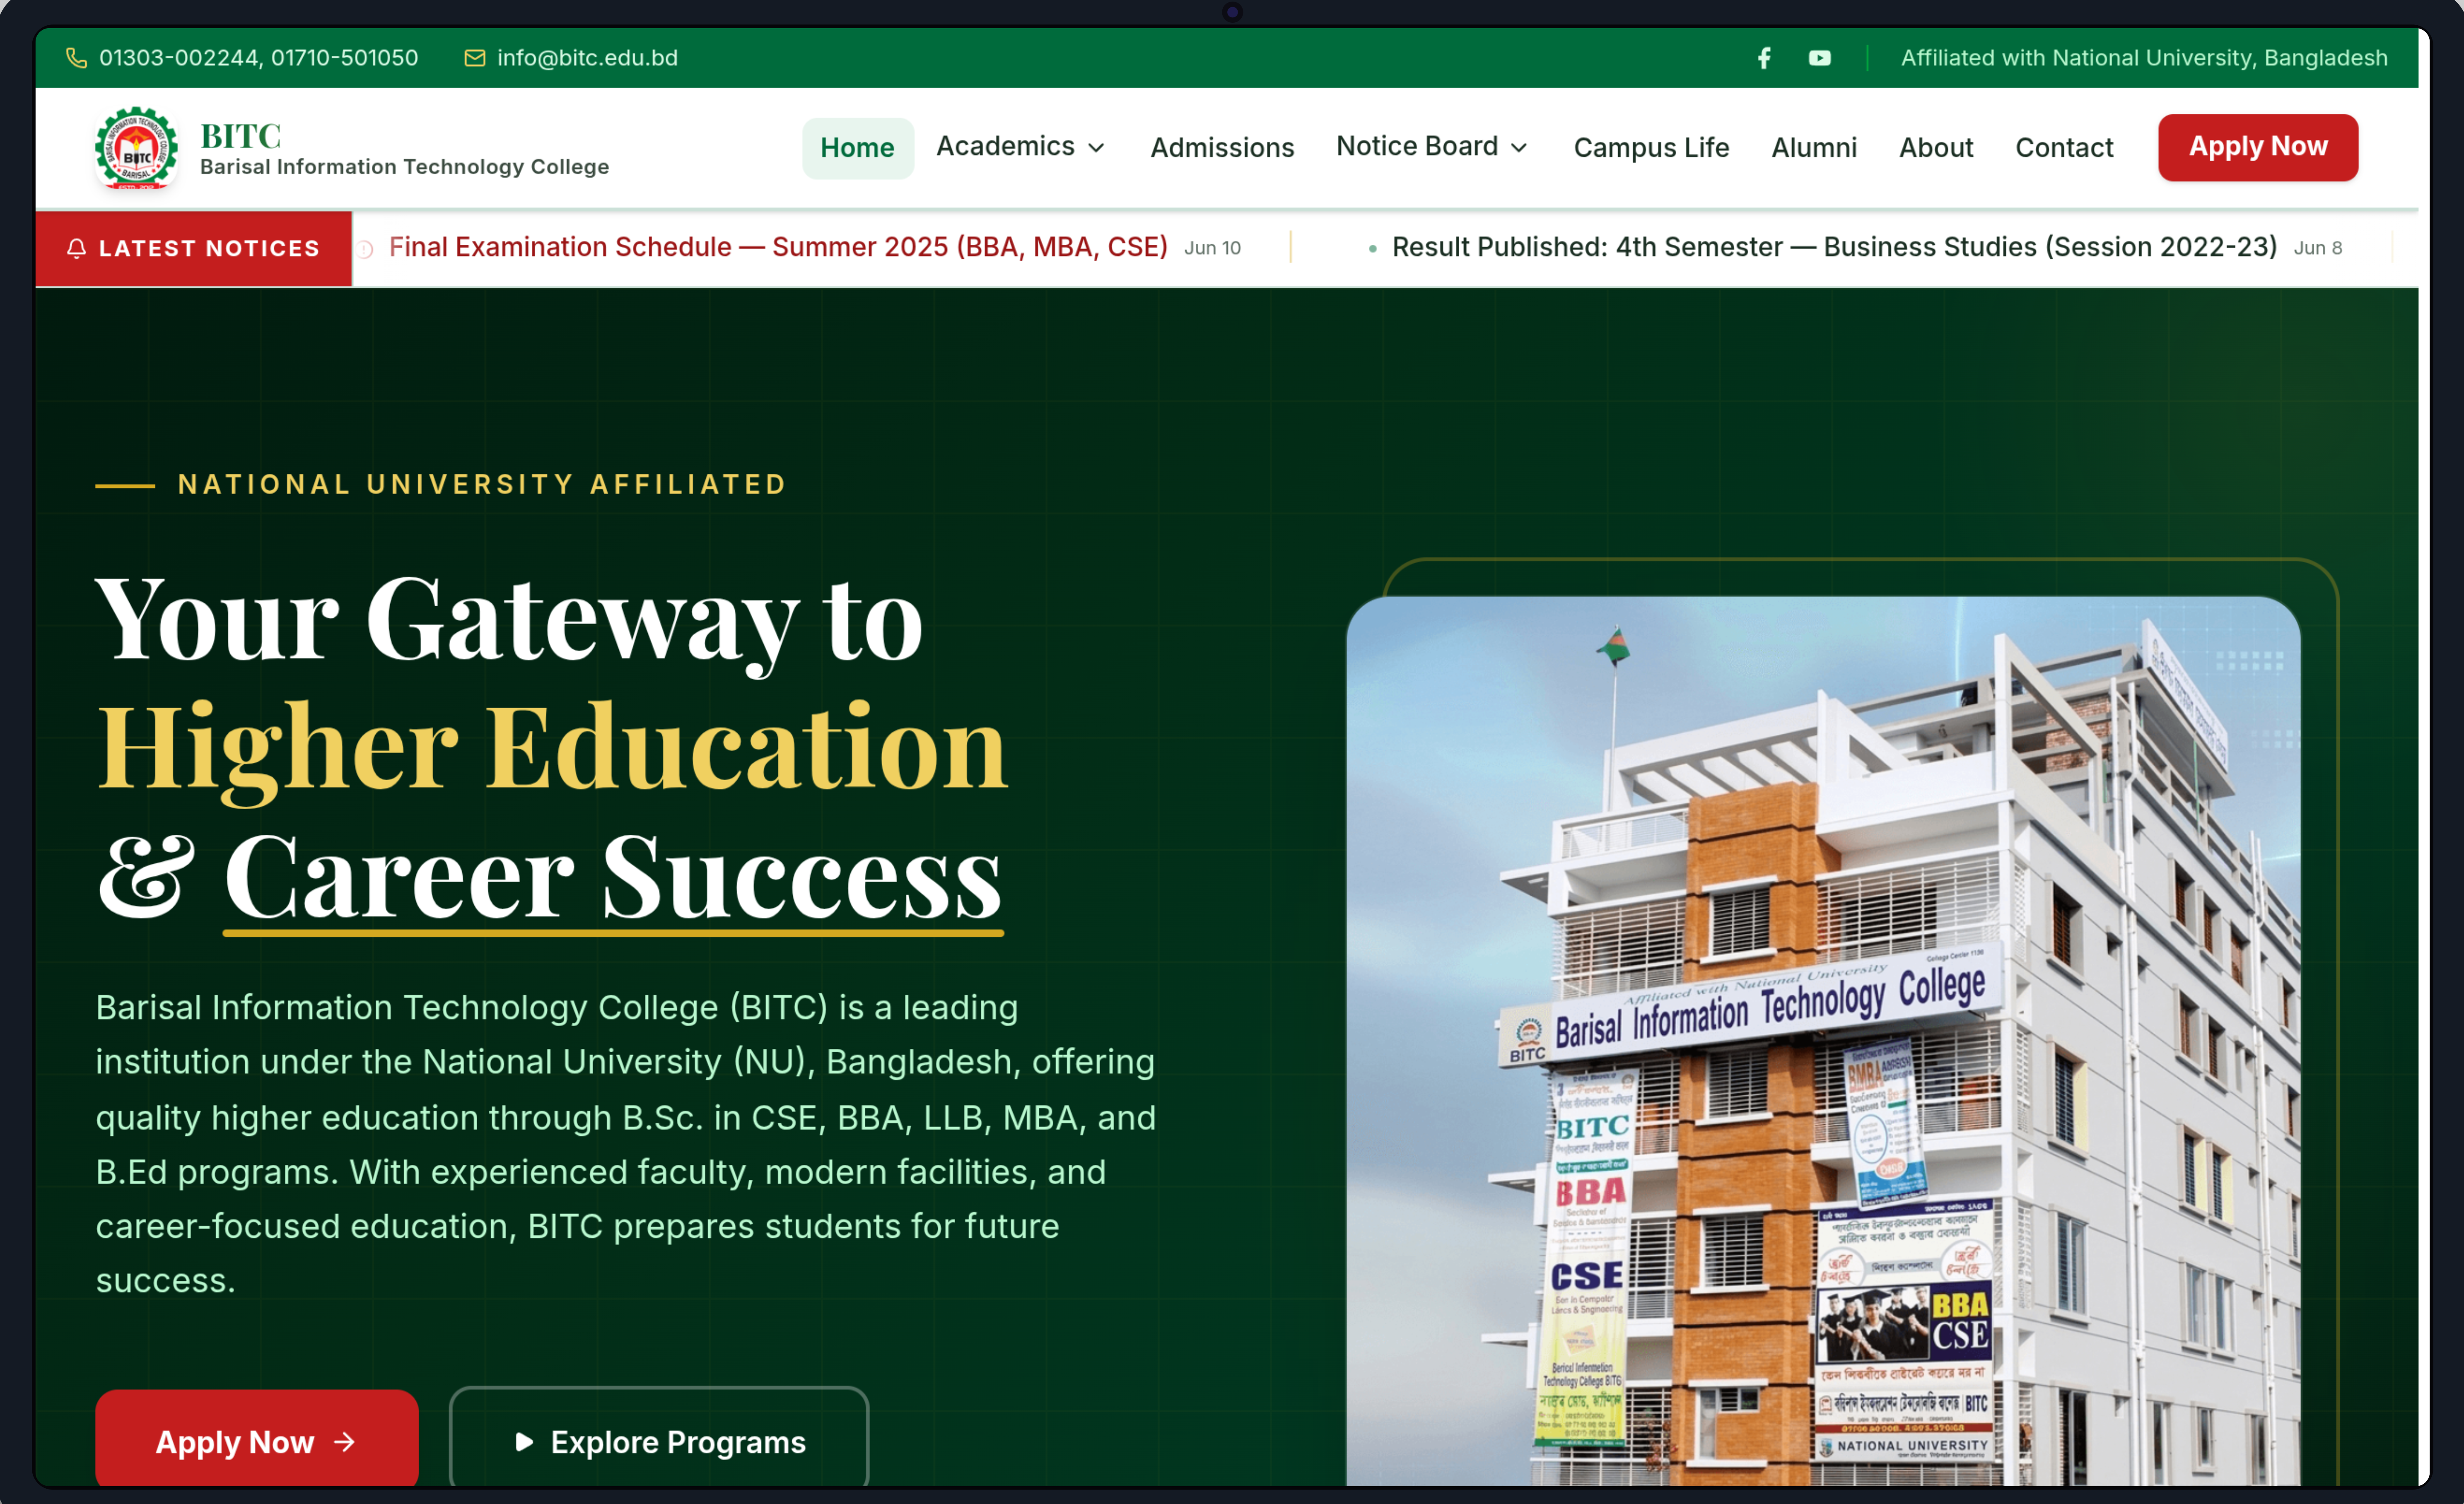
BITC

Web platform developed for Barishal Information Technology College, providing academic notices, department details, admission guidance, and responsive access for students and faculty.
VIEW SITE ↗
FULL-STACKWEB PLATFORMSTRUCTURED UXACADEMIC PORTAL
https://bitc.ac.bd
VIEW SITE ↗
BITC institutional website platform interface
05

ROKTODAN

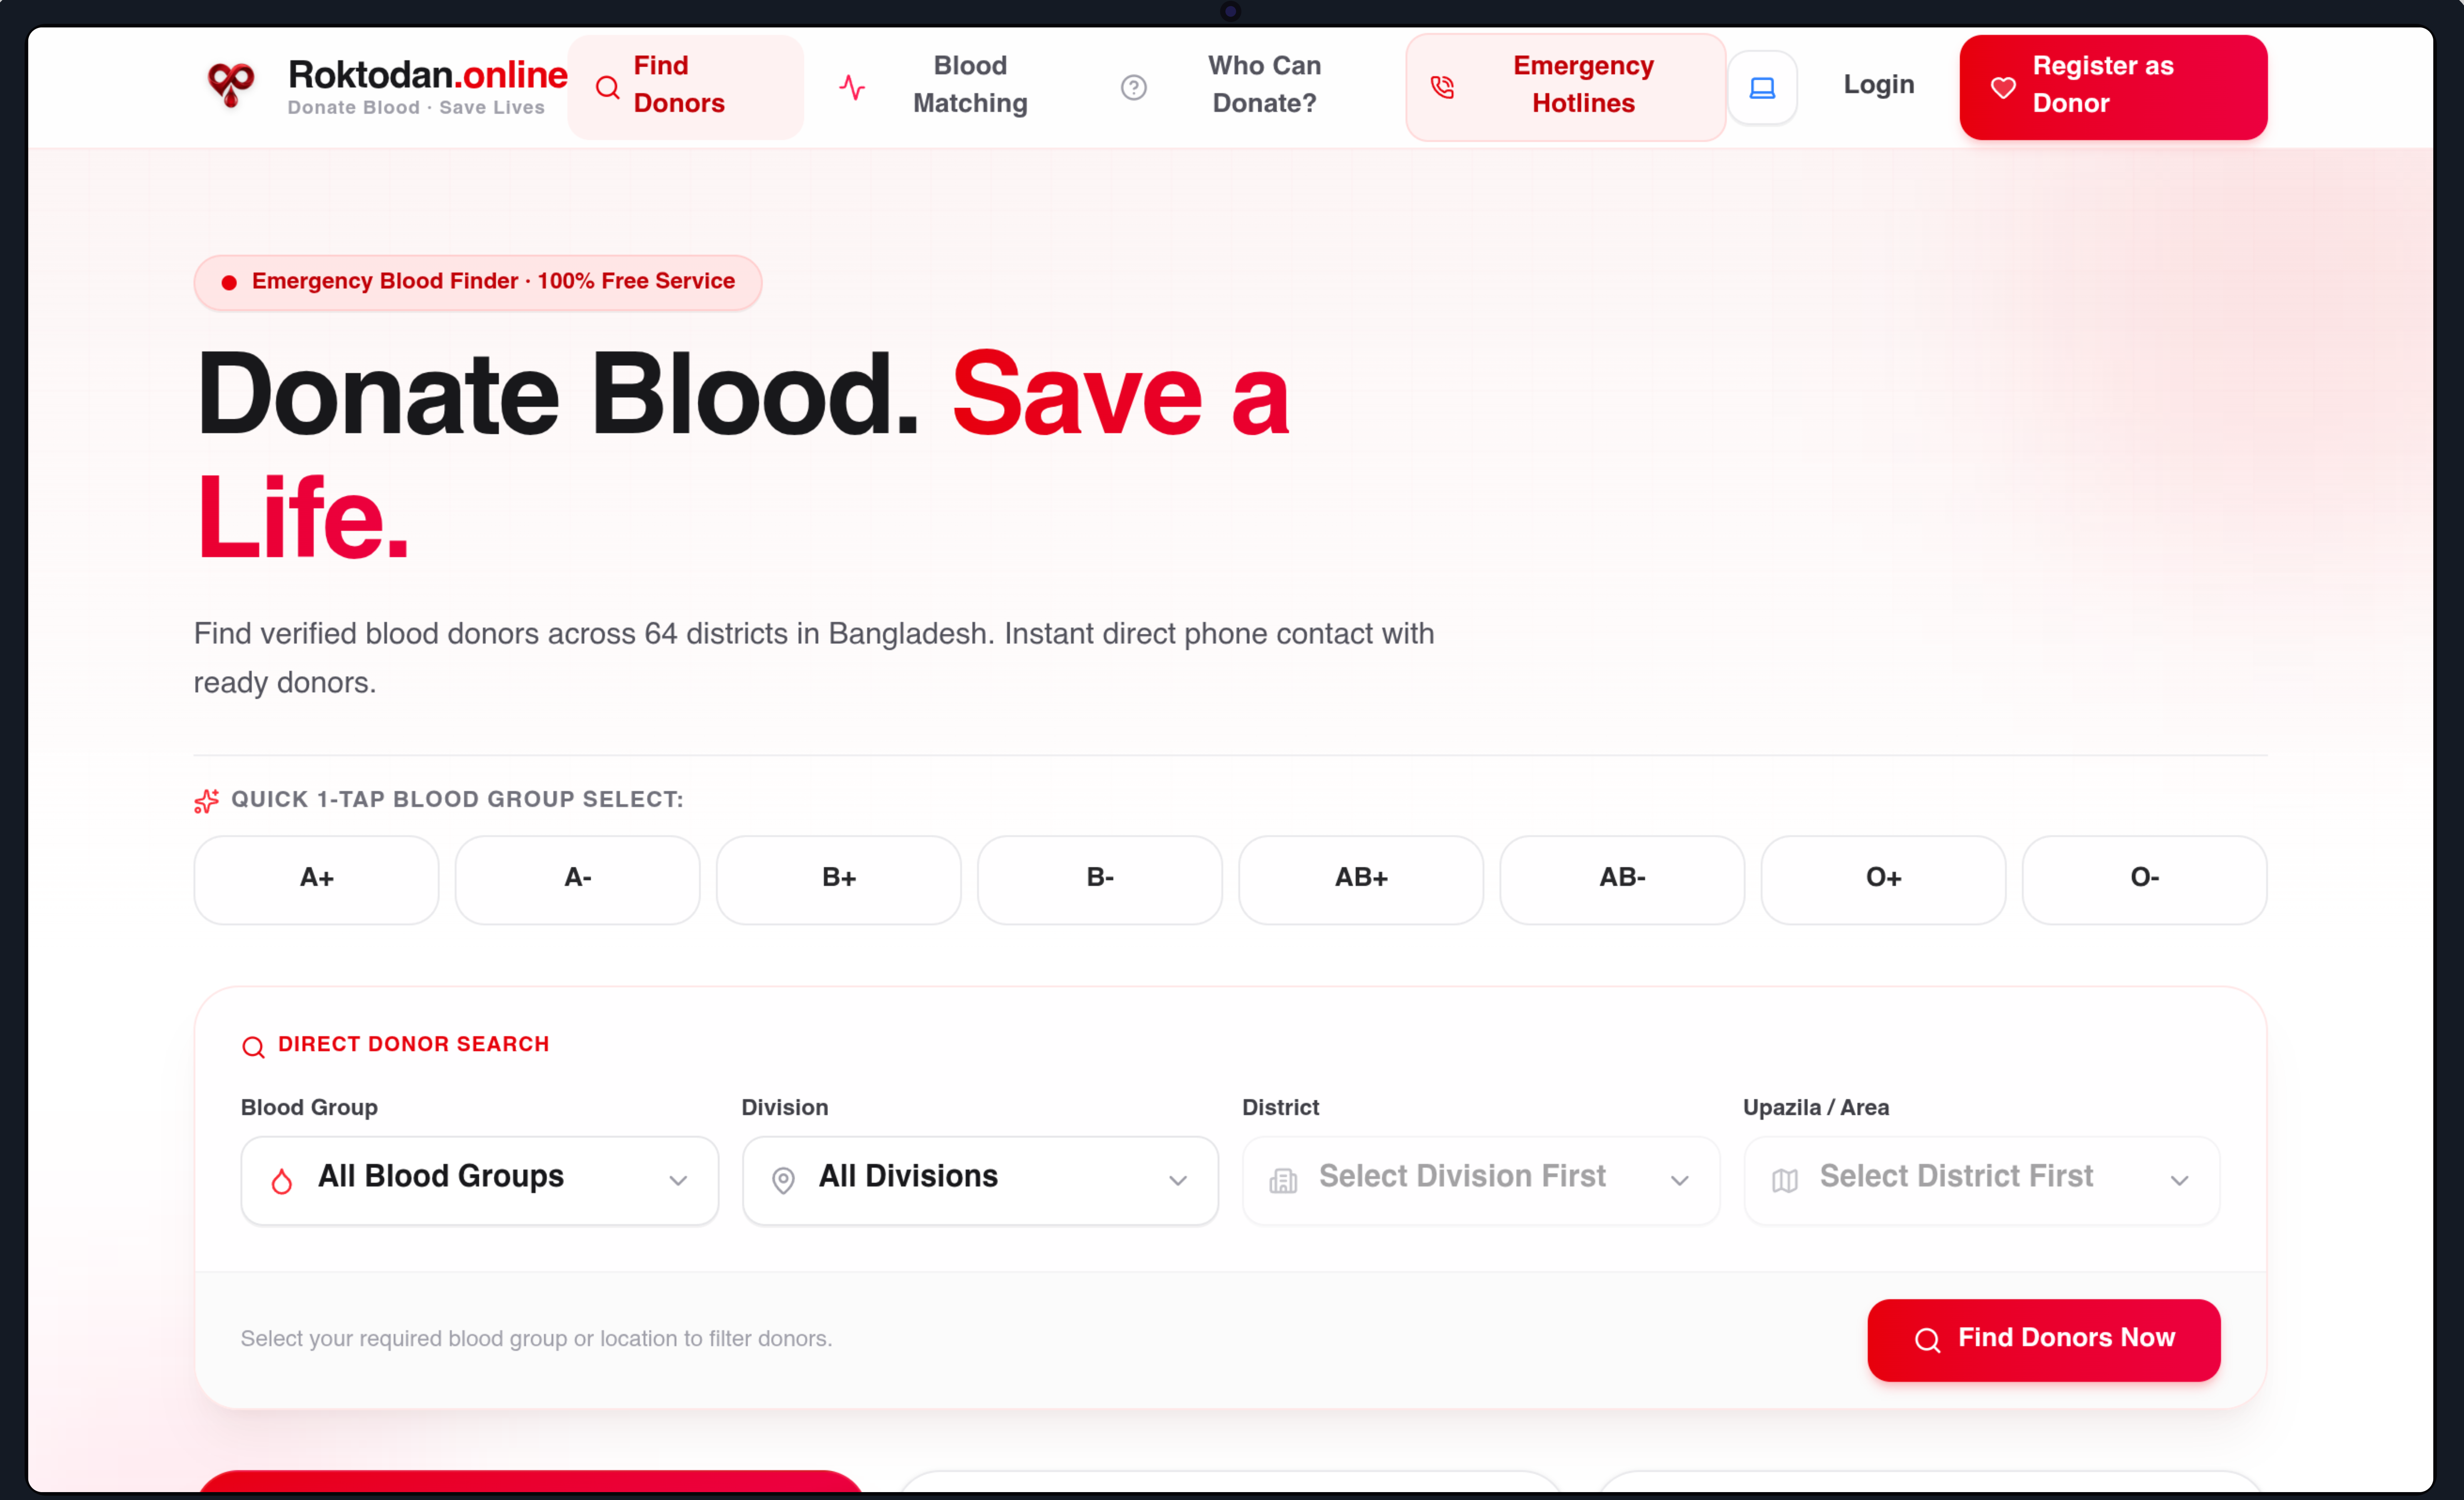
Social-impact web platform developed to help people find voluntary blood donors across Bangladesh by filtering by blood group and district.
VIEW SITE ↗
SOCIAL IMPACTDONOR DIRECTORYBLOOD GROUP FILTERDATABASE
https://roktodan.online
VIEW SITE ↗
RoktoDan social impact donation platform interface
02 / Security work

Proof, not claims.

A sanitized case-study format demonstrating security assessment depth without exposing client-confidential data.
CRITICAL FINDING CASE STUDY

Cloud API
Security Assessment

Sanitized case study from a cloud SaaS environment. Focused on deep authorization testing, tenant isolation, and API access-control logic where automated scanners commonly fail.

BOLA / IDOR (Broken Object Level Authorization)
Multi-tenant SaaS REST API Architecture
Authorization • Authentication • Tenant Isolation
Validated exploit vectors + developer-ready architectural patch guidance
03 / About

Build. Break. Improve.

I'm Md Khaledul Islam — a developer and security engineer operating at the intersection of building software and understanding its failure modes.

I work across application development, security assessment, and custom tooling automation. Balancing development and security helps me understand how applications are assembled from the ground up—and how access controls, business logic, and implementation oversights can be compromised.

My goal is straightforward: build reliable, accessible software and write focused security tools that make workflows simpler and safer.

MD KHALEDUL ISLAM(@khaleddevsec)• ENGINEER
04 / What I do

Engineering with intent.

01

Full-Stack Development

Web applications and platforms built with Next.js, React, and TypeScript, focused on clean architecture, responsive usability, and solid fundamentals.

ReactNext.jsTypeScriptNode.js
02

Web Application Security

Vulnerability assessments and testing focused on business logic flaws, OWASP Top 10 risks, authentication, and authorization vulnerabilities.

OWASPBurp SuiteAPI SecurityVAPT
03

Security Tooling & Automation

Command-line tools and pipelines written in Go and Python to automate reconnaissance, URL filtering, and repetitive security workflows.

GoPythonBashLinux
04

Backend & API Development

RESTful API design, database schemas, and server-side integrations built with security considerations like input validation, rate limiting, and access controls.

ArchitectureREST APIsBackendPostgreSQL
05 / Experience

Where I work.

2025 – Present
Cybersecurity Instructor
Arena Web SecurityVIEW SITE ↗
Teaching practical web security, ethical hacking fundamentals, penetration testing workflows, and mentoring students.
2025 – Present
Co-Founder • Security Team Lead
Cyber ShadowVIEW SITE ↗
Technical leadership, web platform development, and application security assessments.
Ongoing
Full-Stack Developer • Security Engineer
Independent • Client Projects
Developing custom web applications, writing security automation tools, and conducting application security reviews.
06 / Toolkit

The tools are
secondary.

Technologies provide context. The projects and verified security findings provide proof.
TypeScriptJavaScriptReactNext.jsNode.jsPythonGo (Golang)PostgreSQLMongoDBDockerLinux / BashGit / GitHubBurp Suite ProOWASP TestingRESTful APIsVAPTOSINT Tooling
07 / Contact

Let's build
something secure.

Have a product to build, an application to secure, or a security inquiry? Send a confidential message directly through the portal below.